AWS SCPs for a Landing Zone: Guardrails Before You Migrate
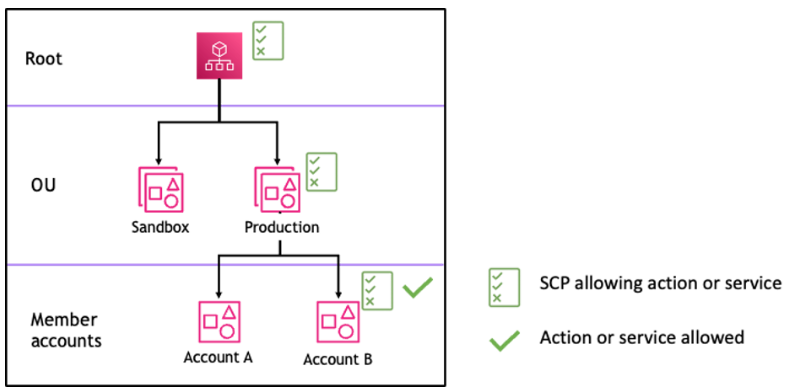
The deny-based Service Control Policies to attach before you migrate workloads into an AWS landing zone, with the config, the deny-list trade-off, and what to check first.
Blog
Notes from real engagements: landing zones, pipelines, on-call, and the security work that gets left until an audit. No thought leadership, no funnels.
The deny-based Service Control Policies to attach before you migrate workloads into an AWS landing zone, with the config, the deny-list trade-off, and what to check first.
The assistant will scope your problem in a couple of minutes.