Enforce IMDSv2 Across an AWS Fleet Without Breaking Workloads
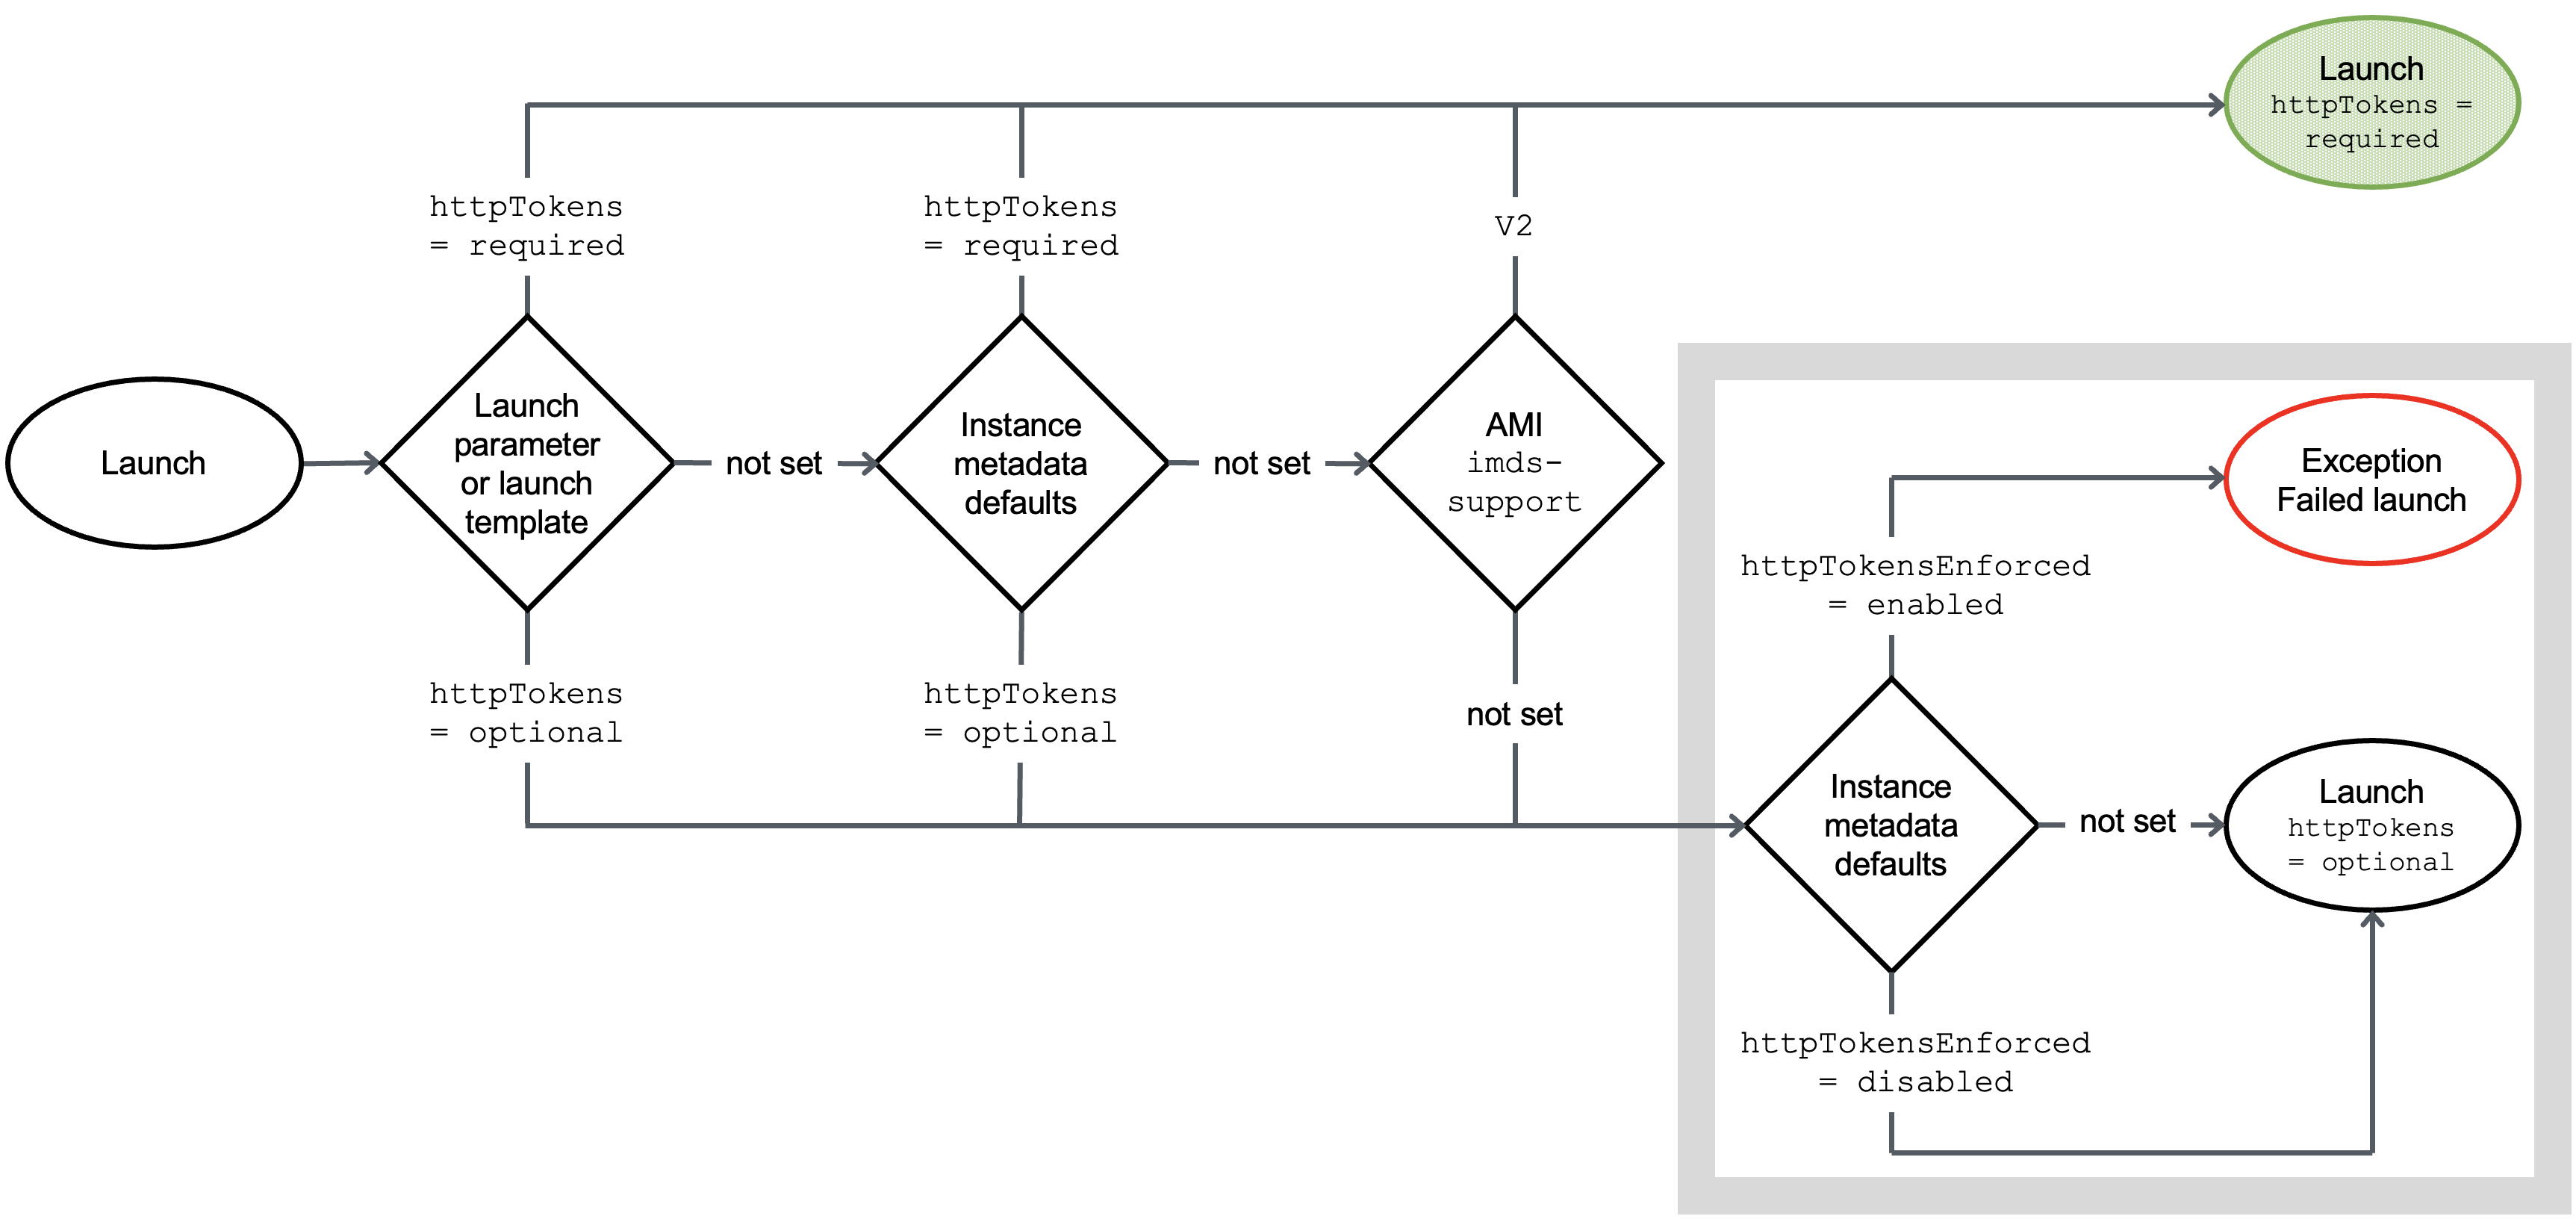
A staged, three-layer plan to require IMDSv2 on every EC2 instance: audit IMDSv1 first with CloudWatch, flip account defaults, then lock it with an SCP.
Blog
Notes from real engagements: landing zones, pipelines, on-call, and the security work that gets left until an audit. No thought leadership, no funnels.
A staged, three-layer plan to require IMDSv2 on every EC2 instance: audit IMDSv1 first with CloudWatch, flip account defaults, then lock it with an SCP.
How to run a full-load-plus-CDC migration with AWS DMS so the cutover window is minutes, not hours, and what to verify on the source before you start.
How to configure fast-burn and slow-burn error-budget alerts on Google Cloud Monitoring and CloudWatch Application Signals, and the trade-off between detection speed and noise.
The assistant will scope your problem in a couple of minutes.